
A blockchain is a digital ledger that many computers hold and update together. New records go into blocks, and each block contains a cryptographic hash of the block before it, so the blocks form a chain. If an old record is changed, its link to every later block breaks. NIST, the US standards agency, puts it this way in its October 2018 overview: "Blockchains are tamper evident and tamper resistant digital ledgers implemented in a distributed fashion." Tamper evident means a change can be detected. It does not mean a change is impossible.
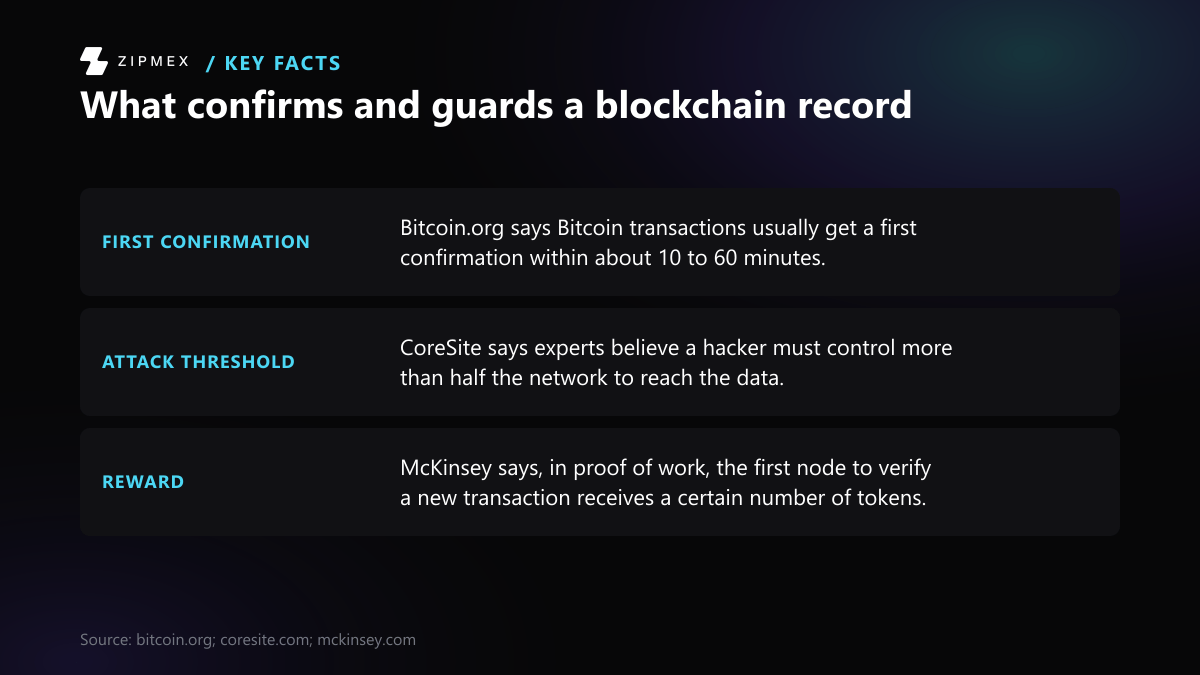

The sections below show how the chain is built and how the computers on the network agree on the next block. They also cover the two main ways public networks secure that agreement: proof of work, which Bitcoin uses, and proof of stake, which Ethereum uses.
How blocks are chained
The idea comes from the Bitcoin whitepaper, published by Satoshi Nakamoto on 31 October 2008. It describes a timestamp server in which "each timestamp includes the previous timestamp in its hash, forming a chain."
In today's Bitcoin software, each block header stores the hash of the previous block's header. The header also holds a merkle root, a single hash that sums up every transaction in the block. The Bitcoin developer documentation states the result: "a transaction cannot be modified without modifying the block that records it and all following blocks."
In practice:
- Editing one transaction changes the merkle root.
- A new merkle root changes that block's hash.
- The next block still points to the old hash, so the chain breaks from that point forward.
Bitcoin.org puts it the same way: the rules "prevent earlier blocks from being changed, because doing so would invalidate every block that comes after."
Who keeps the ledger
The computers that keep a copy of the ledger and check it are called nodes. The whitepaper lists what Bitcoin nodes do:
- New transactions are broadcast to all nodes.
- Each node collects new transactions into a block.
- Each node works on finding a difficult proof of work for its block.
- When a node finds one, it broadcasts the block to all nodes.
- Nodes accept the block only if all transactions in it are valid and not already spent.
- Nodes show they accept the block by building the next block on top of it.
Because every full node checks every block itself, no single operator decides which transactions count. The whitepaper also describes simplified payment verification: "It is possible to verify payments without running a full network node." This is how light wallets work. They check block headers and merkle proofs instead of the whole chain.
Transactions are authorised by digital signatures. Bitcoin.org explains that a wallet holds "a secret piece of data called a private key" and uses it to sign each transaction. The signature also stops anyone from changing the transaction after it has been issued.
How the network agrees: proof of work
On a public network anyone can propose a block. A consensus mechanism decides which proposal wins. In Bitcoin's proof of work, a block header's hash must be at or below a target number. The only way to find such a hash is to keep trying, which costs computing power and electricity.
The figures come from Bitcoin Core's mainnet parameters and Bitcoin.org:
- Block interval: the target spacing is 10 minutes (
nPowTargetSpacing = 10 * 60). Bitcoin.org says blocks are added "approximately every 10 minutes on average." - Difficulty adjustment: every 2,016 blocks, nodes compare the time those blocks actually took with an ideal of two weeks (1,209,600 seconds), then make the target easier or harder.
- Competing blocks: if two valid blocks appear at once, the chain briefly splits. According to the developer documentation, peers "always follow the most difficult chain" and drop the stale blocks from the shorter branch.
- Reward: the first transaction in each block is a generation transaction. It pays the miner the block subsidy plus the fees from that block's transactions. That output cannot be spent for at least 100 blocks.
- Supply schedule: the subsidy halves every 210,000 blocks (
nSubsidyHalvingInterval = 210000). The most recent halving came at block 840,000, mined on 20 April 2024, when the subsidy fell from 6.25 to 3.125 BTC. Bitcoin.org states that the total supply is capped at 21 million bitcoins.
The security assumption is set out in the whitepaper's abstract. The chain stays honest "as long as a majority of CPU power is controlled by nodes that are not cooperating to attack the network." This is where the term "51% attack" comes from: an attacker with most of the mining power could outpace the honest chain and rewrite recent blocks. That is a design threshold, not a measured attack cost.
Why confirmations take time
A transaction enters the ledger only when a miner includes it in a block. Bitcoin.org says transactions "usually receive their first confirmation within about 10 to 60 minutes." It also notes that a low fee can mean a longer wait. Each later block makes the transaction harder to reverse, because an attacker would have to redo all of those blocks.
Proof of work, proof of stake or a permissioned network?
Compare how Bitcoin, Ethereum and Hyperledger Fabric decide who adds the next block, how fast blocks come, when a record counts as settled and what makes an attack costly.
| Network and consensus | Who can take part | How the next block is chosen | Block timing | When a record counts as settled | What makes an attack costly | Source |
|---|---|---|---|---|---|---|
| Bitcoin (proof of work) | Permissionless: virtually anyone can participate | Miners keep hashing until a block header's hash is at or below a target; peers follow the most difficult chain | Target spacing of 10 minutes; difficulty adjusts every 2,016 blocks | First confirmation usually within about 10 to 60 minutes; each later block makes reversal harder | Hardware and electricity; honest only while a majority of CPU power is honest | |
| Ethereum (proof of stake) | Permissionless: a validator deposits 32 ETH and runs the software | Validators propose and vote on blocks with staked ETH as collateral | Slots of 12 seconds; epochs of 32 slots | Final once validators holding two-thirds of all staked ETH vote for it | Collateral the protocol can destroy (slashing of some or all staked ETH) | |
| Hyperledger Fabric (permissioned) | Only known, identified and often vetted participants | Consensus protocols that do not require a native cryptocurrency, under shared governance | Not stated in this article | Not stated in this article | Relies on trust in the members and the legal agreements between them |
This table covers only Bitcoin, Ethereum and Hyperledger Fabric as described in the article; it gives no attack-cost figures, node counts or fee levels, and other networks use different rules.
How the network agrees: proof of stake
Proof of stake replaces computing work with collateral. Ethereum has used it since The Merge on 15 September 2022, which retired proof of work. Ethereum.org estimates the change cut the network's energy use by about 99.95%.
Ethereum's documentation gives the rules:
- Becoming a validator: a user deposits 32 ETH into the deposit contract and runs execution, consensus and validator software.
- Timing: time is split into slots of 12 seconds and epochs of 32 slots.
- Finality: a block counts as final once validators holding two-thirds of all staked ETH vote for it. After that it "can't change without a large amount of ETH getting burned."
- Penalties: a validator who proposes two blocks in one slot, or sends contradictory votes, can lose "some or all of their staked ETH." This is called slashing.
Proof of work makes an attack expensive in hardware and energy. Proof of stake makes it expensive in collateral that the protocol can destroy.
Public and permissioned blockchains
Not every blockchain lets anyone join. The Hyperledger Fabric documentation draws the line:
- Permissionless: "virtually anyone can participate, and every participant is anonymous." Bitcoin and Ethereum work this way.
- Permissioned: the network runs "amongst a set of known, identified and often vetted participants" under a shared governance model.
Permissioned networks can use consensus protocols that "do not require a native cryptocurrency," because nobody needs a token reward to take part. That suits companies sharing records with known partners. In return, they rely more on trusting the members and the legal agreements between them.
What a blockchain does and does not guarantee
- It does: make past changes detectable, let many parties keep one shared record without a central operator, and on public chains, let anyone check the full history.
- It does not: make the data true when it goes in. A false record signed with a valid key is stored like any other.
- It does not: make transactions instant. The wait depends on the block interval and the confirmation or finality rules.
- It does not: make the ledger immune to attack. The guarantees depend on honest participants holding most of the mining power (proof of work) or most of the stake (proof of stake).
Limitations: this explainer covers Bitcoin, Ethereum and Hyperledger Fabric only; other networks use different parameters and consensus rules.
