
An Ethereum smart contract is a program stored at its own address on the blockchain. It does nothing until a transaction calls one of its functions. Every node then runs that code in the Ethereum Virtual Machine (EVM) and checks that it gets the same result. The sender pays for the computation in gas. ethereum.org describes a contract as "a type of Ethereum account". No user controls it. It is "deployed to the network and run as programmed."

What a contract is
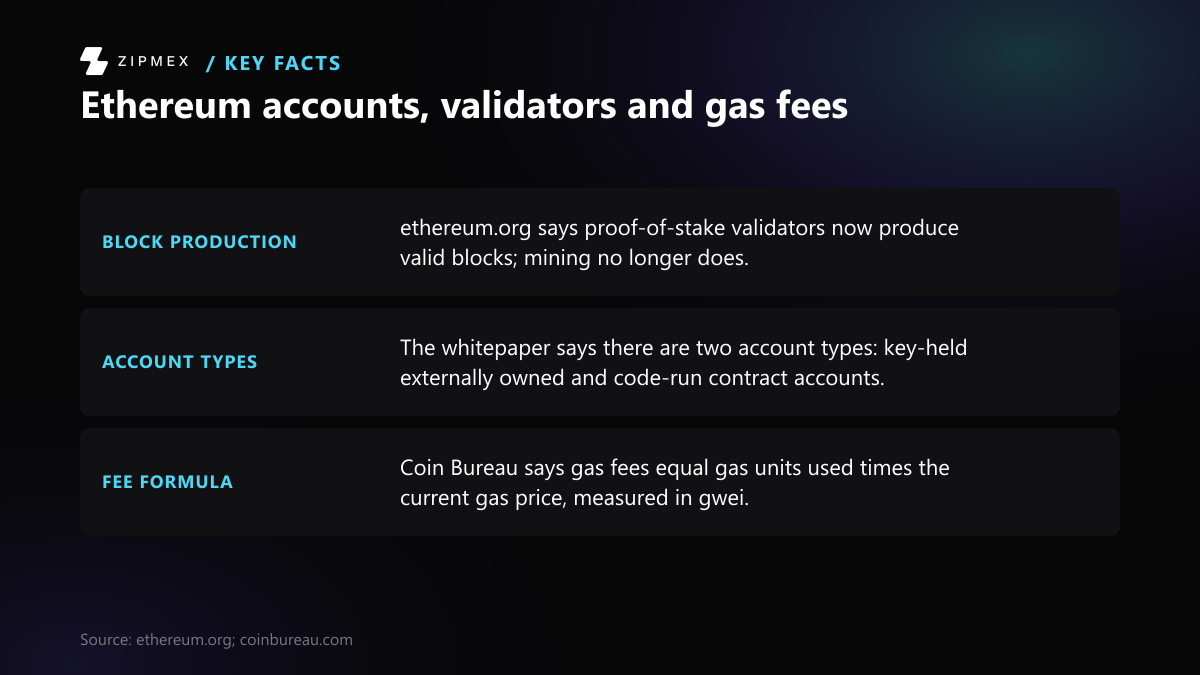
Ethereum has two kinds of account, according to ethereum.org:
- Externally owned account (EOA): "controlled by anyone with the private keys." Creating one costs nothing, and it "can initiate transactions."
- Contract account: "a smart contract deployed to the network, controlled by code." Creating one has a cost because it uses network storage. It "can only send messages in response to receiving a transaction."
Every account has four fields: nonce, balance (in wei), codeHash and storageRoot. For a contract, codeHash points to its EVM code, and ethereum.org says it "cannot be changed, unlike the other account fields." storageRoot commits to the contract's persistent storage. That is where a contract keeps balances, owners, settings and any other state it tracks.
The 2014 Ethereum whitepaper says contracts should not be seen as something to be "fulfilled" or "complied with". It calls them "autonomous agents" that live inside the execution environment, and "every time the contract account receives a message its code activates." That framing still holds. A contract is code that reacts to calls. It is not a legal agreement.
How a call runs
- An EOA signs a transaction to the contract's address. The transaction names a function and its arguments, and it can carry ETH. A contract cannot start itself.
- The EVM executes the bytecode. ethereum.org says "compiled smart contract bytecode executes as a number of EVM opcodes." The EVM is a stack machine "with a depth of 1024 items," and "each item is a 256-bit word."
- The contract can call other contracts. Those calls happen inside the same transaction. ethereum.org compares public contracts to "open APIs" that anyone can build on.
- Nodes agree on the new state. ethereum.org describes the EVM as a state transition function, Y(S, T) = S'. It takes the old state and a set of transactions and produces the new state. Since The Merge on 15 September 2022, proof-of-stake validators propose blocks instead of miners.
Where data lives during a call
- Memory is scratch space that "does not persist between transactions."
- Transient storage is a per-transaction key-value store. It was added by EIP-1153 in the Cancun upgrade on 13 March 2024.
- Storage is persistent and stays in the account's state between calls. It is the most expensive place to write data.
How contracts are written and deployed
Developers rarely write bytecode by hand. ethereum.org lists these languages:
- Solidity: an "object-oriented, high-level language" that is "most profoundly influenced by C++."
- Vyper: a "Pythonic programming language."
- Yul: an "intermediate language for Ethereum."
- Fe: a "statically typed language" "inspired by Python and Rust."
The compiler turns the source into EVM bytecode. ethereum.org notes that "deploying a smart contract is technically a transaction, so you need to pay gas." Anyone can deploy a contract. Contract code is capped at 24,576 bytes. That limit came from EIP-170 in the Spurious Dragon upgrade on 22 November 2016. For larger systems, ethereum.org points to the diamond pattern (EIP-2535).
What the caller pays
ethereum.org gives the fee as:
units of gas used × (base fee + priority fee)
- Gas units measure computation. Each opcode has a gas cost.
- Gwei is one-billionth of an ETH (10^-9 ETH). Fees are usually quoted in gwei.
- Base fee: set by the protocol and burned, which removes it from circulation. This fee market came from EIP-1559 in the London upgrade on 5 August 2021.
- Priority fee (tip): paid to the validator.
- Gas limit: "the maximum amount of gas you are willing to consume on a transaction." Gas you do not use is refunded.
- Max fee: must be higher than the base fee plus the tip, or the transaction is not executed.
Each block targets half of the current block gas limit and can grow to twice the target. The base fee changes with demand, so the same contract call can cost very different amounts from one hour to the next. A separate explainer covers how gas fees are set.
Check a contract before you call it
Answer six quick questions about the contract your wallet wants you to call and see what to check next.
Is your wallet asking you to sign an EIP-7702 delegation for your own address?
- Yes → next question
- No, it is an ordinary contract call → next question
Do you fully trust the contract code that the delegation points to?
- Yes, fully → next question
- No, or not sure → Do not sign the delegation
Have you confirmed the contract address on the project's official pages and on a block explorer?
- Yes, on both → next question
- No → Confirm the address first
Is the contract's source code verified on a block explorer, so the bytecode matches readable code?
- Yes → next question
- No, or I cannot find it → You cannot read what you are calling
Does the contract sit behind a proxy, and who holds the upgrade key?
- No proxy → next question
- Proxy run by a multisig, a timelock or a DAO vote → next question
- Proxy run by a single key → You are trusting the developers
- I cannot tell → You are trusting the developers
Do prices or other outside data drive what the contract does?
The code an EIP-7702 authorization points to has unrestricted access to your account, and a poorly implemented delegate can let a malicious actor take near complete control of it. Treat this request as seriously as a request to hand over your private key.
Check the address on the project's official pages and on a block explorer before you send anything. Interactions with a contract are irreversible.
Without verified source code, you cannot match the bytecode to readable code. You would be calling code you have no way to inspect.
With an upgradeable contract, users must trust developers not to change it arbitrarily. One key can point the proxy to new logic. Multisig control, DAO votes or timelocks reduce that risk.
A contract cannot read the outside world. It depends on an oracle, and that data must be correct for the contract to run correctly. Then check the fee estimate and gas limit in your wallet: a failed call still costs gas.
Fee = units of gas used × (base fee + priority fee). If the call runs out of gas or reverts, the state changes are undone but the gas is still consumed.
This follows the article's pre-call checklist only: it does not audit any specific contract, and it cannot tell you whether a contract is safe or whether to use it.
Mining is no longer the means of producing valid blocks. Instead, the proof-of-stake validators have adopted this role and are now responsible for processing the validity of all transactions and proposing blocks.
When a call fails
ethereum.org says that if a transaction runs out of gas, "the EVM will revert any changes, but all the gas provided will still be consumed for the work performed." A contract can also revert on purpose, for example when a check fails. Either way, the state goes back to what it was before the call, but the sender still pays for the work. The 2014 whitepaper set out the same rule, to "revert all state changes except the payment of the fees." Gas limits also protect the network "to prevent accidental or hostile infinite loops."
What changed in 2025
Pectra, activated 7 May 2025 (EIP-7702). EIP-7702 "allows Externally Owned Accounts (EOAs) to set the code in their account." An EOA owner signs an authorization, and a delegation indicator, 0xef0100 || address, is written to the account's code. Calls to that EOA then run the chosen contract's code in the EOA's own context. This lets an ordinary key-held address batch actions or use other contract logic, so the line between the two account types is less sharp than the original design. The EIP also warns that "the code specified by an authorization has unrestricted access to the account." It says a poorly implemented delegate "can allow a malicious actor to take near complete control over a signer's EOA." Treat any request to sign a delegation as seriously as a request to hand over a private key.
Fusaka, live 3 December 2025. EIP-7825 caps each transaction at 16,777,216 (2^24) gas, so even very heavy contract calls now have a hard ceiling. Clients shipped a 60M default block gas limit, up from 45M. EIP-7939 added a CLZ opcode, which counts leading zero bits. EIP-7883 made the ModExp precompile more expensive for the contracts that use it.
Next: the ethereum.org upgrade timeline lists Glamsterdam as upcoming, with no confirmed date.
What a contract cannot do
- Start itself. An EOA's transaction always starts the call chain.
- Read the outside world. ethereum.org says contracts "cannot get information about 'real-world' events." Ethereum is deterministic, and nodes must agree using only onchain data. Oracles are "applications that source, verify, and transmit external information" to contracts. The contract then depends on that data: it "must be correct for a smart contract to execute correctly."
- Change its own code. Contracts "cannot be deleted by default, and interactions with them are irreversible." Since EIP-6780 (Cancun, March 2024),
SELFDESTRUCTonly fully removes a contract in the same transaction that created it.
How "upgradeable" contracts work
Many projects use a proxy pattern. A proxy contract holds the data and uses the delegatecall opcode to forward calls to a separate logic contract. An upgrade points the proxy to a new logic address. ethereum.org also lists contract migration, data separation, the strategy pattern and the diamond pattern. Its caveat is direct: with upgradeable contracts, "users must trust developers not to modify smart contracts arbitrarily." It suggests multisig control, DAO votes or timelocks to reduce that risk. Before you interact with a contract, check whether it sits behind a proxy and who holds the upgrade key.
What to check before calling a contract
- The address. Confirm it on the project's official pages and on a block explorer.
- Whether the source is verified on an explorer, so the bytecode matches readable code.
- Upgrade control. Is there a proxy, and is the admin a single key, a multisig or a timelock?
- Oracle dependence. If prices or outside data drive the contract, find out where that data comes from.
- The fee estimate and gas limit in your wallet. A failed call still costs gas.
- Any EIP-7702 delegation request. Do not sign unless you fully trust the code it points to.
Limitations: this explainer relies on ethereum.org documentation and the EIP text. It does not audit any specific contract, and protocol details can change with future upgrades.
